
20/09 edition: migrate administrators only when recovery is ready too
An enrolled key does not prove readiness. What evidence allows the old route to be removed without lockout or a weaker recovery path?
- Recovered day
- 2026-09-20
- Actual publication
- 2026-10-05
- Author
- Redação Velqory
- Reviewed
- 05/10/2026 · Europe/Lisbon
- Nature
- Retrospective analysis published on 5 October; it does not represent original publication on the recovered date.
- Operational proposals
- Original, untested Velqory recommendations; hypothetical scenarios, with no claimed internal experience or results.
- Review condition
- Review changes to provider, browser, recovery policy, integration or administration team; test in an authorised environment.
In brief
A migration proposal by administrative route: normal access, backup, recovery and emergency access, with acceptance before expansion.
- Test each administrative route, not only the main login.
- Give recovery an owner different from the person requesting new access.
- Do not declare migration complete while uninventoried alternatives remain.
The decision is to remove the old route
This edition addresses identity teams and owners of privileged access. It asks not whether phishing awareness should continue, but what evidence allows migration of an administrative account without losing recovery capability. This retrospective analysis reports neither a real migration nor an incident on 20 September.
CISA's October 2022 fact sheet recommends that administrators and other high-value targets implement or plan migration to phishing-resistant MFA. This is US technical guidance, not a Portuguese duty established here. Velqory's proposed priority is a bounded administrative route whose alternatives are understood.
Not every second factor is phishing-resistant
CISA's table distinguishes FIDO/WebAuthn and PKI-based authentication from one-time codes and number-matching notifications. The latter remain described as vulnerable to phishing. 'It has MFA' is not a sufficient answer to the migration question.
WebAuthn Level 2, the April 2021 W3C Recommendation, describes public-key credentials scoped to the relying party. This supports the mechanism distinction, but does not validate your service configuration. This article does not compare products or claim that a credential makes a user, session or entire system immune.
Choose one administrator and one service
Original Velqory proposal: choose a service whose team can support the pilot. Record portal access, administrative tooling, alternative devices and any emergency route. Exclude machine identities from this exercise: they need their own analysis, not an artificially assigned physical key.
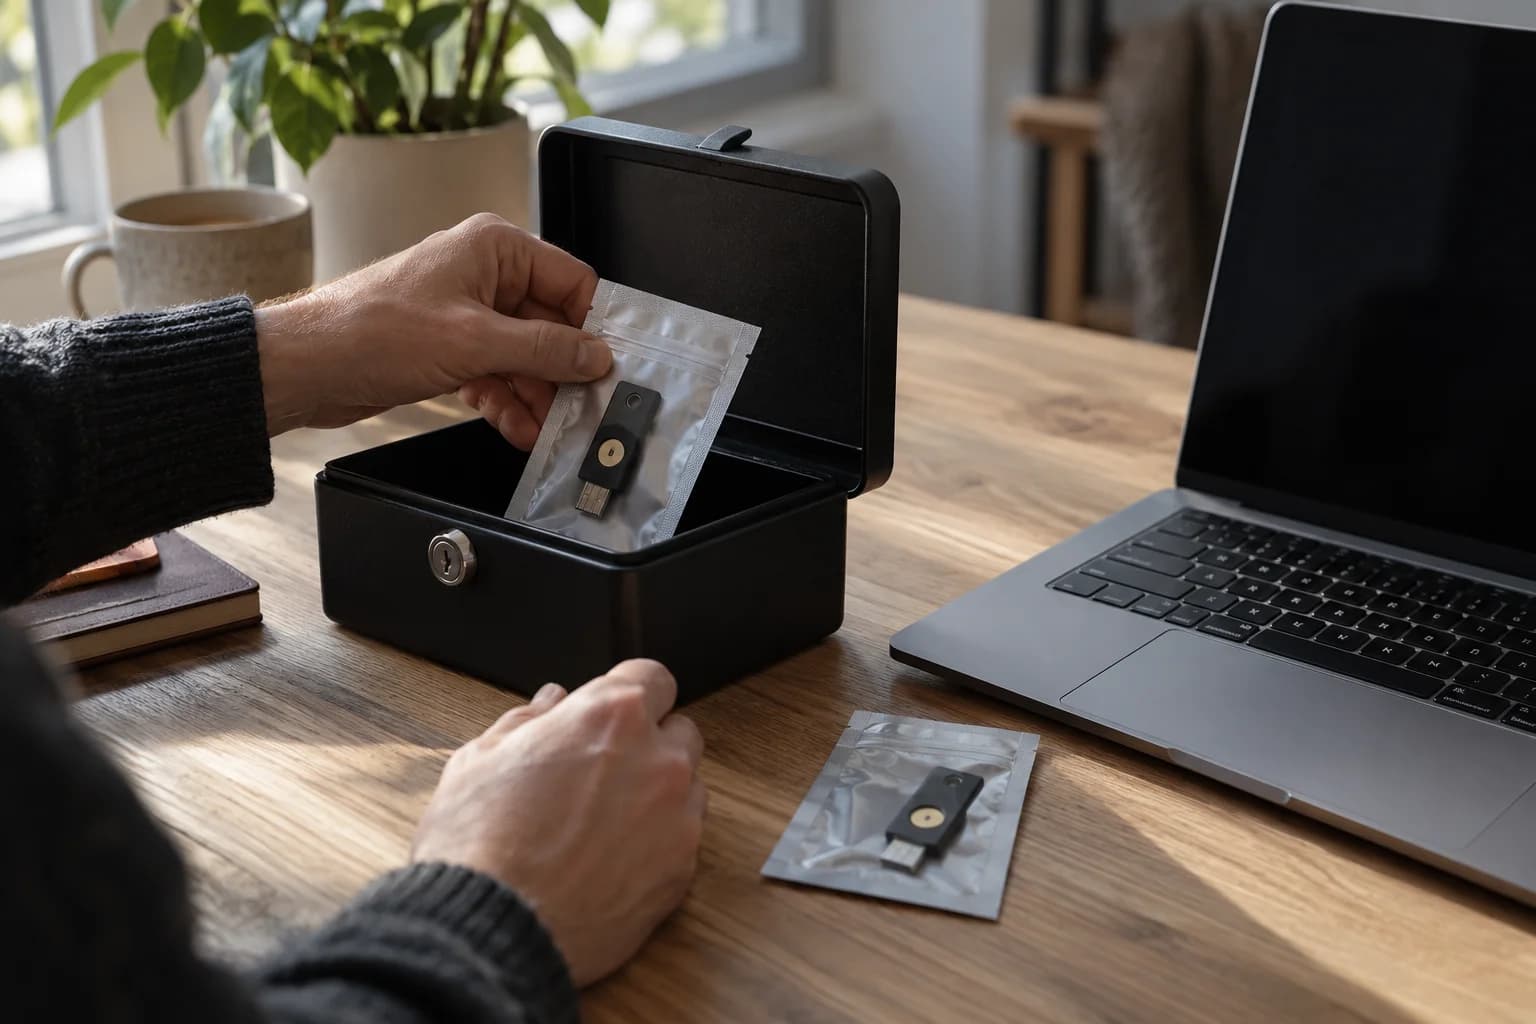
Before changing normal access, prepare a backup authenticator and authorised recovery. Specify who verifies identity, approves replacement and can observe the change. Do not place credentials, backup codes or secrets in the dossier; retain test identifiers and results with limited access.
Readiness to cut the previous route
These proposed tests have not been executed and need adaptation to the service documentation. Use a test account and authorised environment. Passing one row does not replace the others; an unknown alternative should result in 'not ready', not a silently partial migration.
Acceptance by administrative route
Neither a certified procedure nor a security guarantee.
| Route | Owner | Evidence | Pass / fail |
|---|---|---|---|
| Normal access | Identity | Result and applied policy | Method enforced / only enrolled. |
| Backup | Test administrator | Login using backup authenticator | Works within intended scope / depends on primary. |
| Lost authenticator | Support and approver | Request, verification and decision | Identity verified / email alone suffices. |
| Emergency | Security owner | Exercise and observed alert | Restricted, visible use / permanent exception. |
| Legacy removal | Service owner | Review of every route | Alternatives handled / portal alone. |
The key was lost during an absence
Hypothetical scenario: an administrator loses the authenticator and the deputy is absent. Support receives an urgent email requesting restored access. The exercise asks whether identity can be recovered under the approved rule without improvising a weaker method than normal access.
If the team must remove authentication requirements for the whole group to solve one case, the pilot fails our proposed criterion. Record the obstacle and adjust recovery before expanding. Any necessary exception needs scope, an approver and a removal condition, without presenting it as a mechanism tested by this editorial team.
Proceed only with a documented decision
CISA identifies incompatible systems and phased implementation among migration obstacles. We propose turning those obstacles into questions for the service owner, without assuming a provider's current support. Retain configuration version and documentation consulted when the exercise takes place.
Decide whether to proceed, repair recovery or defer cutting an identified route with approved compensating measures. Our editorial recommendation measures readiness through recoverable access and governed alternatives. The aim is not a photograph of distributed keys: it is an administrative account whose operation and recovery can be explained without an indispensable individual.
Sources consulted
Consulted on the stated update date.
Opens in a new window.Participate
Share the analysis. Add context.
Distribute the article through your channel or leave an observation connected to the topic.
Comments
Loading the conversation.