Latest edition

Regulation, AI and cybersecurity, with sources in view.

Context for better decisions.

Analysis on AI, cybersecurity, regulation, governance and digital systems. With sources, practical consequences and one clear next action.

All analyses

253–264 of 267

Current knowledge, organised by topic, date and practical consequence.

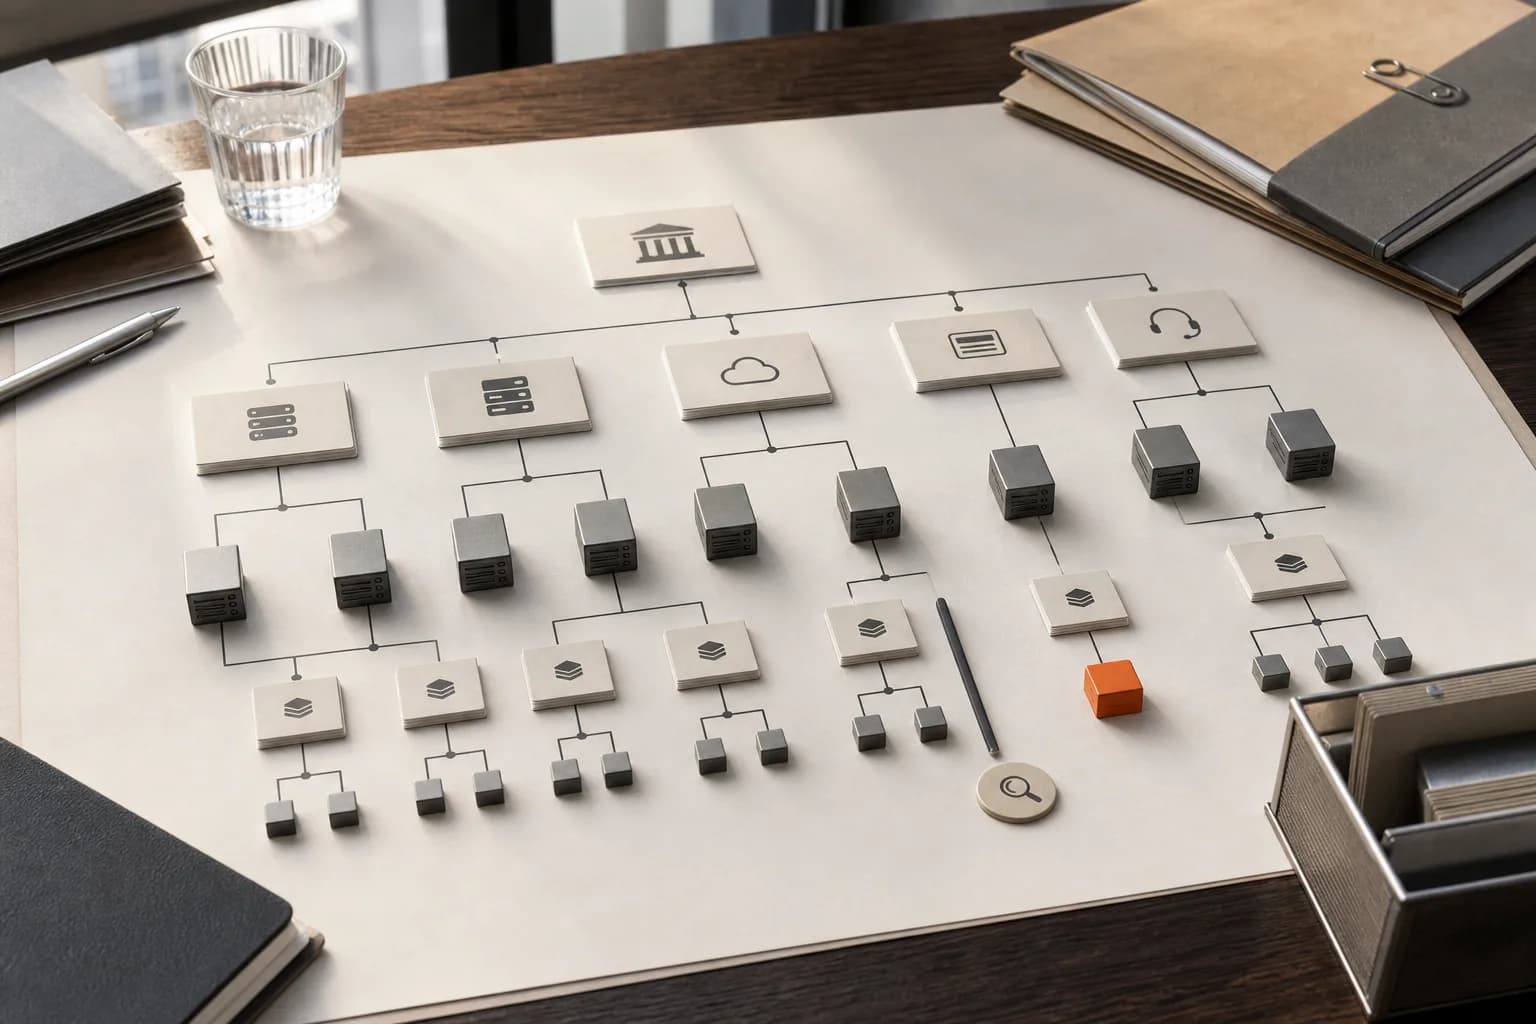
Tiered physical map connects a financial entity to ICT services, providers, and subcontractors
The DORA register should reconstruct contracts, services, functions, and dependencies — not merely list suppliers.AI-generated image under Velqory editorial direction.
Governance15 min read

DORA: the ICT provider register is a dependency map, not a contact sheet

Article 28 requires a register of every contractual arrangement for ICT services, and Implementing Regulation 2024/2956 sets the templates. The real 2026 challenge is keeping keys, relationships, and supply-chain tiers complete enough for supervision and operational risk.

Read analysis
Generic connected device accompanied by exportable structured data and metadata components
After 12 September 2026, data access becomes a verifiable property of the product and its related service.AI-generated image under Velqory editorial direction.
Regulation14 min read

Data Act: data access in connected products placed on the market after 12 September 2026

The Regulation already applies. For the first product placed on the market after 12 September 2026, Article 3(1) turns format, metadata and access by default into product requirements — not a future portal enhancement.

Read analysis
Generic storage modules connect primary data to an isolated copy and a recovery key
A copy does not prove recoverability: identity, isolation, integrity, and actual recovery time also need evidence.AI-generated image under Velqory editorial direction.
Cybersecurity15 min read

Storage security: the NIST draft only pays off when recovery is tested

SP 800-209r1 is open for comment until 8 September. It is a voluntary technical draft — not a Portuguese legal obligation — but it offers a useful opportunity to test whether snapshots, backups, identities, and dependencies survive the same incident.

Read analysis
Generic mobile object accompanied by selectively presented digital attribute cards
The 2026 rollout requires technical preparation, but Member State provision and private acceptance do not run on the same clock.AI-generated image under Velqory editorial direction.
Digital systems15 min read

EUDI Wallet: what a relying party should prepare for the end-2026 rollout

End-2026 is the Member State provision deadline, not a universal business-acceptance duty. A relying party should classify itself, close registration and attribute requests, and test integration before confusing readiness with legal obligation.

Read analysis
Cryptographic locking components joined by connectors representing dependencies between systems
The PQC transition starts by discovering cryptographic dependencies and testing interoperability, not by blindly replacing algorithms.AI-generated image under Velqory editorial direction.
Cybersecurity16 min read

PQC in the European Union: the roadmap has started, but it did not create a general company deadline

The roadmap recommends that Member States start transitioning by the end of 2026 and that critical infrastructure move by 2030. These are EU roadmap milestones, not a horizontal corporate obligation: the immediate work is cryptographic discovery, long-lived data prioritisation, and supplier testing.

Read analysis
Team examines a generic device and organises a three-stage response sequence
The reporting deadline is executable only when product, trigger, territory, decision and evidence are already connected.AI-generated image under Velqory editorial direction.
Cybersecurity13 min read

Cyber Resilience Act: the reporting clock starts on 11 September

The Commission issued new guidance on 27 July and updated its operational page yesterday. Before the remaining 2027 duties apply, hardware and software manufacturers must already report actively exploited vulnerabilities and severe incidents within 24 and 72 hours.

Read analysis
Team tests a generic payment terminal with flow cards and unbranded components
The digital euro is in technical preparation: value now lies in testing interfaces and dependencies without treating a project as a launched product.AI-generated image under Velqory editorial direction.
Digital systems12 min read

Digital euro: rulebook 0.91 prepares a pilot — not a launch

The ECB published documents yesterday covering standards, integration and a 12-month pilot. Version 0.91 already supports technical mapping, but issuance depends on EU legislation and a later decision by the ECB Governing Council.

Read analysis
Conceptual installation of connected modules and a system opened for inspection
Useful enforcement readiness starts with knowing the organisation's role and the evidence it can produce.AI-generated image under Velqory editorial direction.
Artificial intelligence12 min read

EU AI Act on 2 August: enforcement begins for general-purpose AI models

Tomorrow the Commission gains effective powers over applicable obligations for providers of the most advanced models. The AI Omnibus delayed high-risk rules, not the entire regulation: this guide separates roles, dates and evidence.

Read analysis
Hands inspect a module from a generic disassembled device on an organised workbench
The right to repair requires teams to separate covered product, responsible operator, time, price and consumer evidence.AI-generated image under Velqory editorial direction.
Regulation11 min read

Right to repair: the EU deadline passed — and Portugal needs confirmation

Directive (EU) 2024/1799 had to be transposed and applied from 31 July. The EUR-Lex database consulted today shows zero measures notified by Portugal; that is a verification alert, not permission to invent national law.

Read analysis
Two people analyse a conceptual service dependency map at a table
NIS2 preparation starts by making critical services, dependencies, decisions and implementation evidence visible.AI-generated image under Velqory editorial direction.
Regulation22 min read

NIS2 in Portugal: the operational dossier that separates deadlines, duties and evidence

Decree-Law 125/2025 is in force and Regulation 756/2026 made the regime operational. This guide explains who must act, what management must decide, how incident reporting works and what evidence should exist.

Read analysis

Each analysis links to the official source and says what changes in practice.

  1. 01Sources in view

    Every analysis links the official documentation it relies on.

  2. 02Operational context

    We translate change into decisions, owners and evidence.

  3. 03Continuous review

    We update the analysis when facts or guidance change.

  4. 04Identified imagery

    We disclose generated photography and credit documentary photography.

Is there an obligation or a system that needs to become operational?

We map the problem, write the scope and build the solution with acceptance criteria.